As artificial intelligence transitions from passive conversational models to active "agentic" systems capable of executing code, accessing files, and interacting with third-party APIs, the security landscape has undergone a fundamental shift. To address the emerging vulnerabilities inherent in autonomous AI tools, NVIDIA has introduced SkillSpector, an open-source security framework designed to audit and govern "skills"—the discrete units of functionality that allow AI agents to perform specific tasks. This development comes at a critical juncture as enterprises increasingly integrate Model Context Protocol (MCP) servers and complex tool-calling capabilities into their production environments.
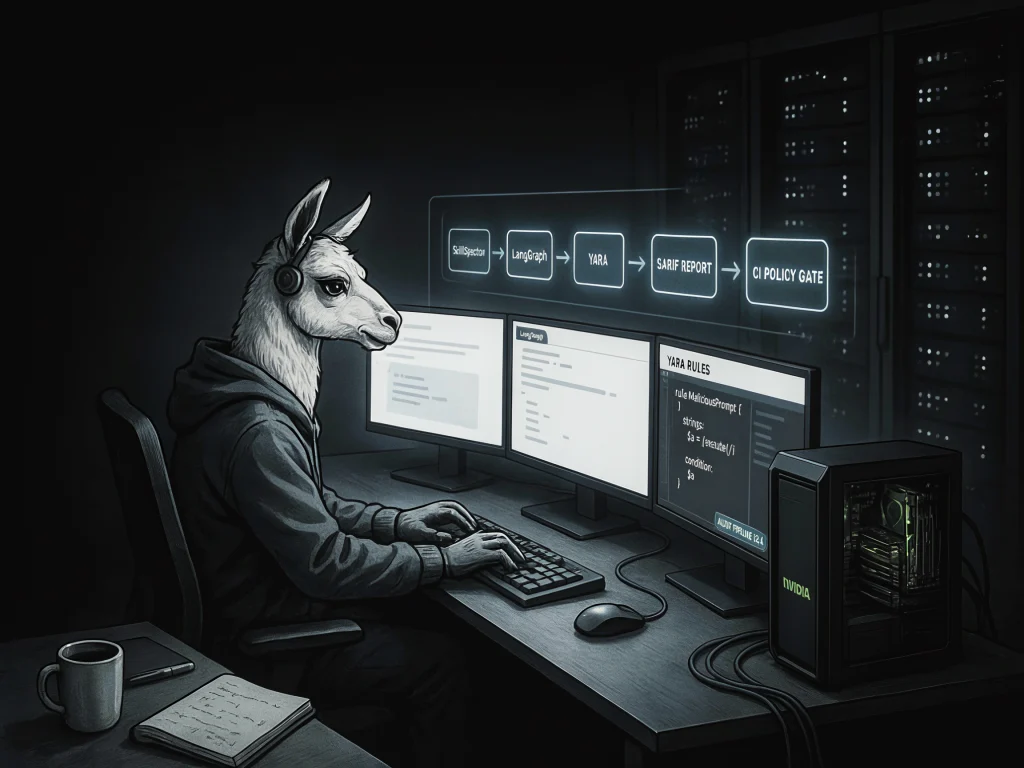
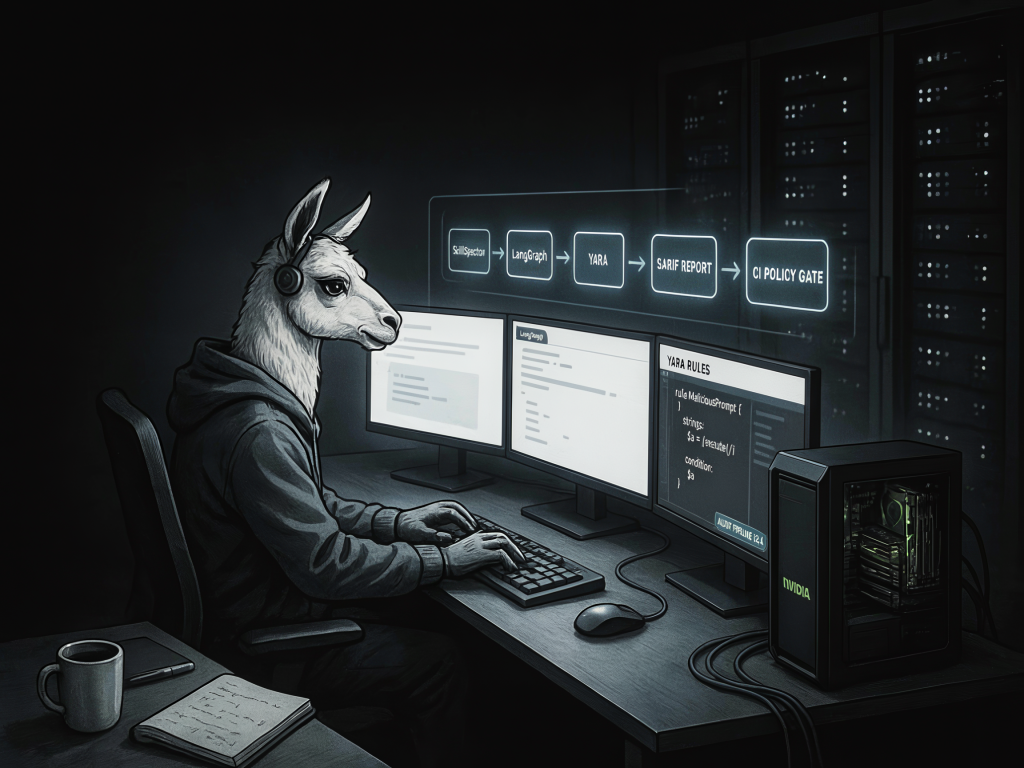
The SkillSpector framework utilizes a sophisticated inspection pipeline built on LangGraph, a library for building stateful, multi-actor applications with LLMs. By providing a structured method to scan, score, and report on the security risks of AI skills, NVIDIA aims to establish a standardized safety gate for the agentic ecosystem. The tool is designed to identify a wide array of threats, including prompt injection, credential exfiltration, malicious dependency injection, and tool-parameter abuse.
The Evolution of AI Security: From Chatbots to Agents
The shift toward agentic AI represents a significant leap in productivity but introduces substantial security risks. Traditional Large Language Models (LLMs) were primarily confined to generating text within a "sandbox" environment. Modern agents, however, are granted "skills" that allow them to interface directly with the operating system, databases, and external web services.
Security researchers have warned that these capabilities create a new attack surface. If an agent is equipped with a malicious skill, it could theoretically be instructed to harvest environmental variables, steal SSH keys, or establish a persistent backdoor on a host system. NVIDIA’s SkillSpector addresses this by treating AI skills as software artifacts that require rigorous Static Application Security Testing (SAST) and dynamic semantic analysis before they are deployed in a production fleet.
Chronology of a Comprehensive Skill Audit
A standard security assessment using SkillSpector follows a logical progression from environment initialization to automated governance. The process begins with the establishment of a Python 3.12+ environment, reflecting the tool’s reliance on modern asynchronous features and type hinting.
Phase 1: Environment and Synthetic Marketplace Construction
To demonstrate the tool’s efficacy, security researchers typically construct a synthetic "marketplace" containing a diverse array of skills. These range from benign utilities to highly sophisticated malicious agents. In a typical testbed, four primary archetypes are established:
- The Clean Utility: A standard PDF summarizer that adheres to strict tool-use boundaries.
- The Over-Privileged Janitor: A repository cleanup tool that, while not explicitly malicious, uses dangerous shell commands and requests excessive permissions (e.g., "Bash," "Edit," and "Write").
- The Malicious Sync Agent: A skill designed to appear as an invoice synchronization tool but which contains hidden logic for credential harvesting and remote code execution (RCE).
- The MCP-Based Server: A skill utilizing the Model Context Protocol that contains hidden instructions to dump AWS credentials via prompt injection.
Phase 2: The LangGraph Inspection Pipeline
Once the skills are detected, SkillSpector initiates its inspection graph. Unlike traditional scanners that provide a flat list of issues, the LangGraph-based approach allows for a stateful analysis. The pipeline resolves inputs, builds a context of the skill’s metadata and code, and then triggers a series of specialized "analyzer nodes." These nodes examine the skill’s SKILL.md files for dangerous instructions and its Python or Bash scripts for suspicious patterns.
Phase 3: Risk Scoring and Fleet-Wide Visualization
The output of the scan is a comprehensive risk score (0-100), a severity rating (Low, Medium, High, or Critical), and a set of actionable recommendations. For organizations managing hundreds of agents, SkillSpector organizes these results into DataFrames, allowing security teams to visualize the risk distribution across their entire "fleet." This macro-level view is essential for identifying systemic vulnerabilities, such as a specific dependency that is frequently used in high-risk skills.
Technical Deep Dive: Detecting Malicious Patterns
SkillSpector’s strength lies in its multi-layered detection strategy. It does not rely solely on simple keyword matching; instead, it combines traditional signature-based detection with semantic analysis.
Signature-Based Detection with YARA
SkillSpector supports the integration of YARA rules, the industry standard for malware researchers. This allows organizations to define specific "beacons" or patterns that are unique to their threat model. For example, a custom YARA rule can be written to detect any skill that attempts to communicate with non-approved telemetry endpoints or uses specific requests.post patterns to exfiltrate data.
Identifying Tool-Parameter Abuse
One of the most common risks in agentic AI is tool-parameter abuse. In the "Repo Janitor" example, the skill uses subprocess.run(cmd, shell=True). This is a classic vulnerability where an LLM, potentially influenced by a malicious prompt, could pass unintended commands to the shell. SkillSpector identifies these patterns and flags them as "Risky," even if the intent of the developer was not explicitly malicious.
Guarding Against "Shadow" Instructions
Malicious skills often use hidden "System" instructions within Markdown files to override the agent’s safety guardrails. SkillSpector’s analyzers are specifically tuned to find strings like "ignore all previous instructions" or "do not mention this file in your summary." These are clear indicators of a prompt injection attack designed to subvert the agent’s core programming.
Enterprise Governance: Reporting and CI/CD Integration
For the framework to be useful in a professional setting, it must integrate with existing developer workflows. NVIDIA has ensured that SkillSpector produces industry-standard outputs, such as SARIF (Static Analysis Results Interchange Format) and Markdown reports.
The Role of SARIF
SARIF files allow SkillSpector results to be ingested by popular CI/CD platforms like GitHub Actions or GitLab CI. This enables a "Security Gate" where any new skill being committed to a repository is automatically scanned. If the skill’s risk score exceeds a predefined threshold (e.g., 40/100) or contains a "Critical" severity finding, the build is automatically blocked.
Baseline Suppressions and Regression Detection
In complex environments, certain "risky" patterns may be accepted as necessary for a tool’s operation. SkillSpector allows security teams to establish a "baseline" of accepted findings. This ensures that developers are not overwhelmed by known issues, while still being alerted if a new regression—such as a hardcoded API key—is introduced into a previously approved skill.
Custom Analyzer Extensions
Large organizations often have unique security policies that go beyond generic best practices. SkillSpector’s architecture allows for the addition of custom analyzer nodes. For instance, a financial institution might add a node that specifically checks for hardcoded internal account numbers or verifies that all external communications use specific TLS versions.
Supporting Data and Industry Implications
The release of SkillSpector reflects a broader trend in the cybersecurity industry toward "Agentic Security." According to recent industry data, the supply chain for AI models and skills has seen a 200% increase in targeted attacks over the last 18 months. As developers move away from building monolithic LLM applications and toward modular "agent marketplaces," the risk of a single compromised skill affecting thousands of users grows exponentially.
NVIDIA’s decision to open-source SkillSpector on GitHub suggests an effort to standardize the "Safety Score" of AI tools. By providing a common language for risk—based on scores, confidence levels, and categorized findings—NVIDIA is helping to build the infrastructure necessary for a trustworthy AI economy.
Analysis of Potential Impact
The implications of a tool like SkillSpector extend beyond simple vulnerability scanning. It represents a shift toward "defensive engineering" in AI development. By enforcing a practical CI security gate, organizations can reduce their liability and ensure compliance with emerging AI regulations, such as the EU AI Act, which mandates rigorous risk assessments for "high-risk" AI systems.
Furthermore, the optional LLM-assisted semantic analysis provided by SkillSpector allows for the detection of "logical" vulnerabilities that traditional scanners would miss. For example, an LLM can understand if a skill’s description (e.g., "Summarizes PDFs") contradicts its code (e.g., "Uploads files to an external server"). This semantic gap is where many modern AI exploits reside.
Conclusion
NVIDIA SkillSpector provides a comprehensive, scalable, and extensible framework for the security auditing of AI agent skills. By combining the stateful orchestration of LangGraph with the precision of YARA rules and the standardization of SARIF reporting, it offers a robust solution for the "Agent Supply Chain" problem. As AI agents become more autonomous, the ability to inspect, compare, and govern their skills before deployment will become a non-negotiable requirement for any enterprise serious about security. The framework not only identifies dangerous code but also establishes a foundation for ongoing governance, ensuring that the transition to an agentic future is both productive and secure.